
Data protection & secure digitalisation
Use data deliberately.
Set clear technical boundaries.
DAXS implements agreed legal and operational requirements in technology: from forms and access rights to cloud services, integrations and AI tools. The central question is which system may use which data for which purpose.
Clear responsibilities
Data protection is not a single product setting.
Legal and data-protection advisors establish the applicable requirements. The organisation decides on purposes, workflows and approvals. DAXS translates those requirements into technical configuration, roles, data flows, logging and secure operating processes.
Services
From requirements to day-to-day operation.
Map data flows
Make sources, recipients, integrations, storage locations and access visible across forms, email, files, CRM, ERP and other business systems.
Implement access rules
Configure users, roles, sharing, MFA and administrative responsibilities to match the actual workflow.
Secure forms
Consider necessary required fields, TLS, secure uploads, permitted file types, spam protection, recipients, logging and retention together.
Review cloud and SaaS
Define which data may enter Microsoft 365, Google Workspace, business applications or other services and how it can be recovered or removed.
Use AI in a controlled way
For Copilot, Gemini, OpenAI/ChatGPT services or API integrations, clarify per process which content may be processed, retained or excluded.
Operate the lifecycle
Connect retention, deletion, backup, recovery, logging and recurring controls in the technical design.
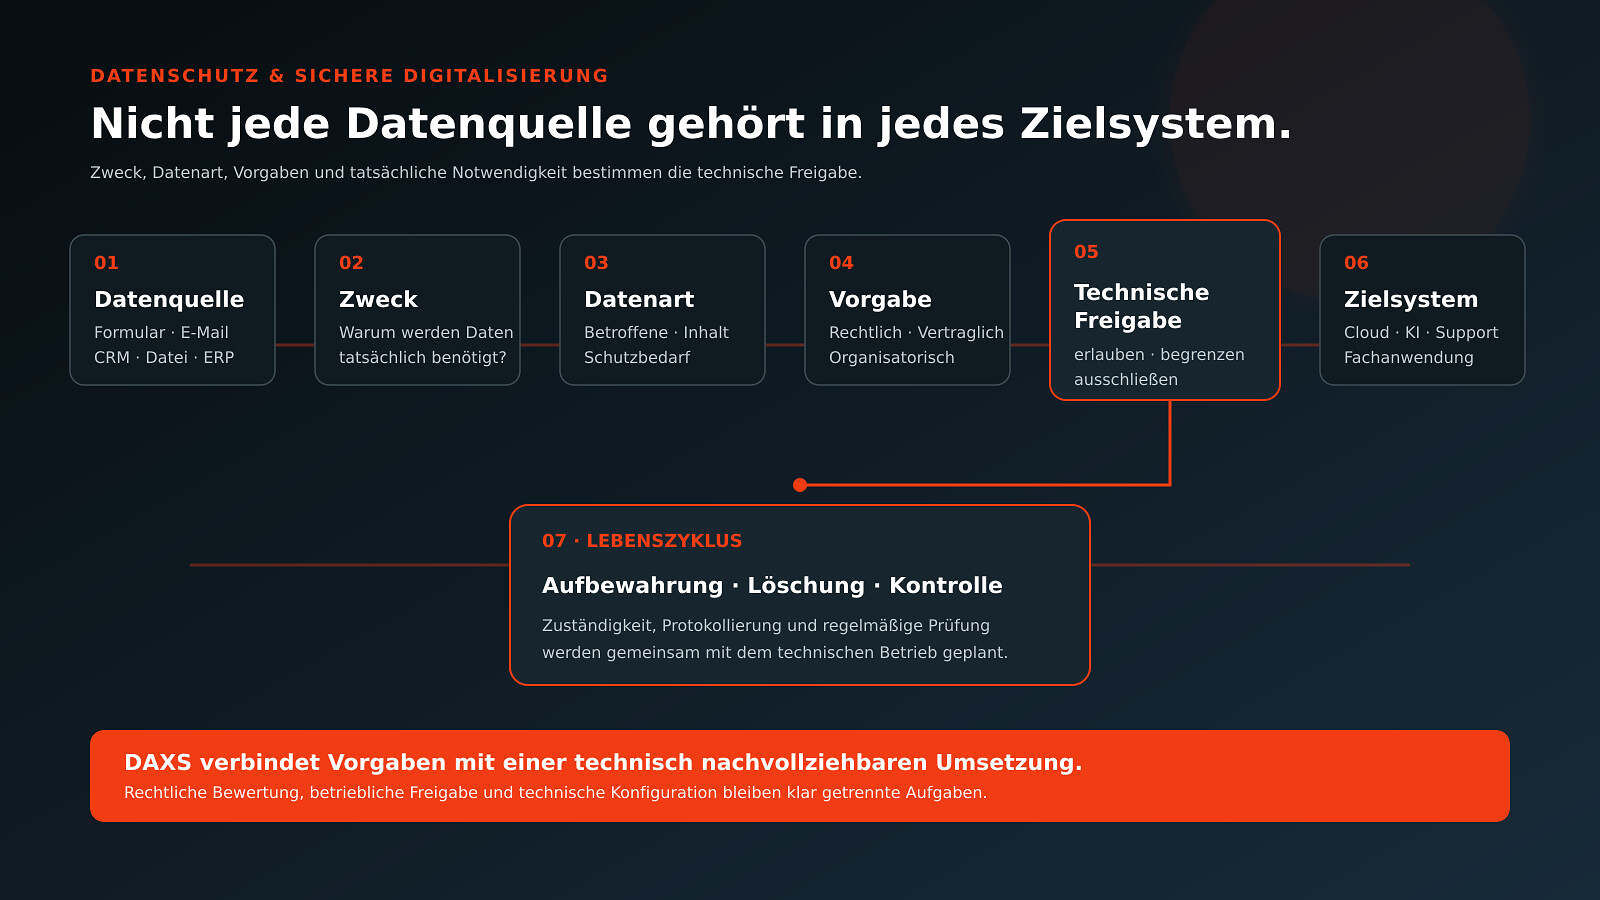
Data approval
A clear decision comes before configuration.
System access is not appropriate simply because it is technically possible. Purpose, data type, sensitivity and agreed requirements determine whether data is allowed, limited or excluded.
Web forms
Consent is not automatically the right answer.
An extra checkbox does not automatically make a data process compliant. Purpose, necessary fields, legal basis and recipients must be established first. Only then can the required notice or consent be determined.
DAXS implements the agreed workflow and considers uploads, file formats, transport encryption, logs, deletion periods and spam protection.
Related topics
Connected, but kept distinct.
Data protection
Requirements, purposes and permitted processing.
IT security
Protection of systems, identities and access.
Backup
Data protection and tested recovery.
AI governance
Approval, use and control of specific AI processes.
Which data may go where?
We capture the technical baseline, map data flows and implement agreed requirements in a traceable way.
Discuss secure digitalisation